
Nearly $15B is moving off LayerZero, now a $292M lawsuit puts its security model on trial
Evercrest Technologies, the company behind KelpDAO, has sued LayerZero Labs, its Canadian affiliate, and CEO Bryan Pellegrino in British Columbia over April's $292 million rsETH exploit. The claim alleges negligent misrepresentation, negligence and defamation, seeks aggravated and punitive damages, and says Kelp users have withdrawn more than $650 million since the attack. Pellegrino has called […] The post Nearly $15B is moving off LayerZero, now a $292M lawsuit puts its security model on trial appeared first on CryptoSlate.
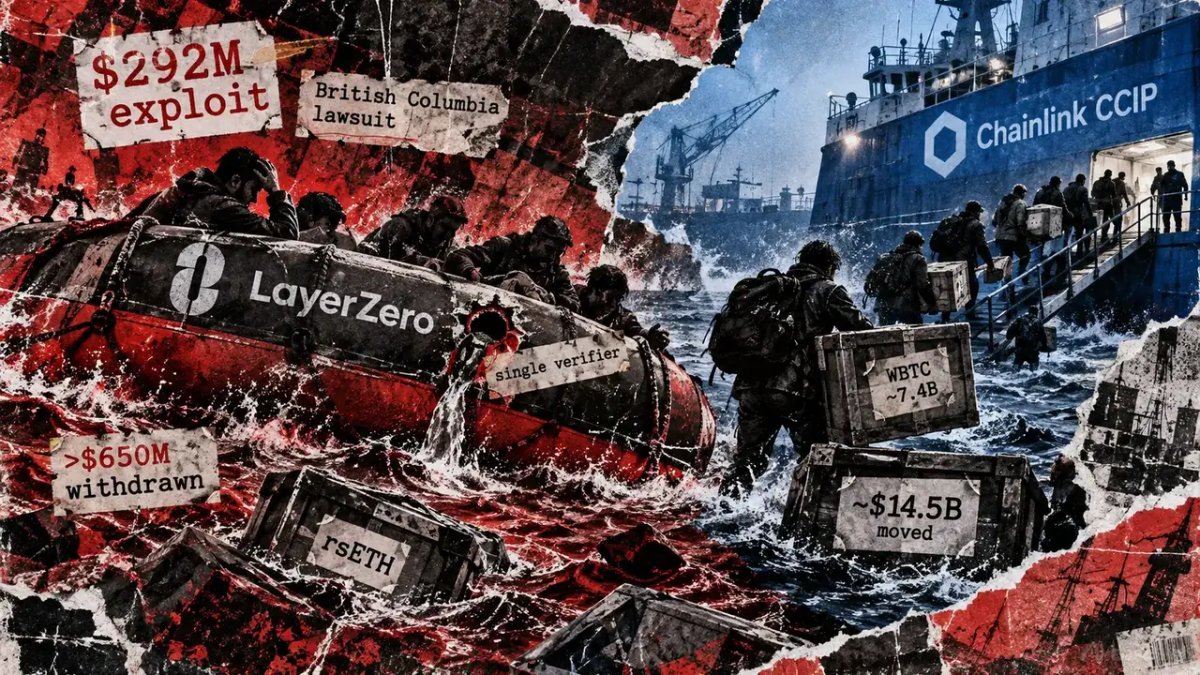
Evercrest Technologies, the company behind KelpDAO, has sued LayerZero Labs, its Canadian affiliate, and CEO Bryan Pellegrino in British Columbia over April's $292 million rsETH exploit.
The claim alleges negligent misrepresentation, negligence and defamation, seeks aggravated and punitive damages, and says Kelp users have withdrawn more than $650 million since the attack.
Pellegrino has called the suit meritless. By Aug. 4, projects tied to roughly $14.5 billion in assets had announced moves from LayerZero to Chainlink's CCIP, nearly 50 times the amount stolen.
The lawsuit now asks a court to settle a responsibility dispute that customers have been pricing on their own since April.
On April 18, attackers tricked LayerZero's verifier into approving a forged cross-chain transfer. LayerZero's incident report traces the intrusion to a developer who was socially engineered into cloning a malicious GitHub repository in March.
The attackers reached LayerZero's RPC environment, poisoned two internal nodes, and knocked an external RPC provider offline, so the verifier signed a message built on false source-chain data and 116,500 rsETH left Kelp's bridge.
That compromise succeeded because Kelp's bridge required approval from a single verifier, LayerZero's own, leaving one party able to authorize the release. The on-chain signature check worked as designed, since the signature was valid and simply attested to false information.
LayerZero's report splits the blame accordingly, assigning the number of required verifiers to the application and the compromised RPC layer to LayerZero as its operator.
| Security layer | What was supposed to happen | What failed | Who controlled that layer |
|---|---|---|---|
| Verifier count | Multiple independent verifiers could reject a bad message | Kelp required only LayerZero's verifier | Application / Kelp |
| RPC data | Verifier receives accurate source-chain state | Attackers poisoned LayerZero-operated RPC infrastructure | LayerZero |
| Independent check | A second verifier could disagree with false data | No second required verifier existed | Application configuration |
| Signature generation | Verifier signs only valid source-chain events | LayerZero's verifier signed false data | LayerZero-operated verifier |
| On-chain contract | Accept valid signatures from configured verifier set | Worked exactly as configured | Smart contract logic |
Evercrest alleges LayerZero reviewed and approved the single-verifier setup in writing, including telling Kelp in February 2024 there was “no problem” with a default configuration.
The suit also alleges LayerZero warned another developer, USDT0, about risks in default verifier configurations while withholding a comparable warning from Kelp.
Those allegations have yet to be tested in court. LayerZero's account puts the choice on Kelp, saying the application had previously used a two-of-two configuration and moved to one-of-one.
LayerZero's verifier now refuses to sign on any channel where it's the only required signer, and the company requires multiple independent RPC sources across providers and geographies.
By Aug. 4, it had moved default pathways on both versions of its endpoint to a minimum of three verifiers, while applications can still build custom setups at the protocol level.
LayerZero also said in May that letting its own verifier act alone on high-value transfers had been a mistake, and it maintained the incident touched about 0.14% of the applications on its network.
BitGo accounted for the largest migration, with WBTC making up about $7.4 billion of the Aug. 4 tally, and it named CCIP its exclusive cross-chain provider for WBTC and the default for future BitGo-issued assets.
Mantle, Kelp's rsETH and Lombard added billions more, and Chainlink puts the total near $15 billion. Kelp says its own migration remains underway, so announced value and completed transfers are separate measures.